IanTwenty
- 3 Posts
- 12 Comments
Joined 1 year ago
Cake day: October 17th, 2025
You are not logged in. If you use a Fediverse account that is able to follow users, you can follow this user.

 11·11 days ago
I do not run Immich but their privacy policy states:
Locally Stored Data: Immich stores all your photos, albums, settings, and other metadata locally on your device. We do not have access to this data, nor do we transmit or store it on any of our servers.
https://immich.app/privacy-policy
Additionally in their docs I can find no mention of connecting to outside services. I do see references to downloading hugging face models.
https://docs.immich.app/features/facial-recognition#how-face-detection-works
 35·14 days ago
Potentially the server can request hardware/software attestation that would limit the choice of password safe to approved ones only. We don’t yet know how big/likely this could be, but in theory it’s possible.
This is what people seem to be missing, I haven’t seen a rebuttal to this problem.
I think the worry is that if passkey attestation is required it will force people into a narrow set of authenticators controlled by the big orgs.
At this point in time it’s not a problem, but how can we know it won’t be in future?
I agree 100%, this post is not a full rebuttal and does not tackle the concerns directly:
- The character of the organisations in FIDO does not inspire confidence against lock-in or monopolistic behaviour
- The possibility of future attestation cutting out those on ‘unapproved’ software and hardware.
I agree parts of the tech are good, particularly the anti-phishing, anti-replay measures.
This post seems to say passkeys are in good hands so nothing can go wrong, but I don’t think that’s enough.
The phishing attack could also try to convince you your bank had changed domains (hey we’ve been bought by Big Bank and will be moving your account to BigBank.com) and therefore not to expect your password manager to autofill (this is a stretch I know).
Passkeys are resistant to phishing as they cannot be replayed and your authenticator should refuse challenges from the wrong domain. Even if it did solve a challenge from bigbank.com it’s worthless as the origin is included in the returned challenge so cannot be used by the attackers on the real bank site.
Maybe one extra thing you are missing is passkeys are resistant (not proof) to phishing. The user returns an ‘assertion’ that:
uses the private key to digitally sign a challenge value from the server, together with contextual information such as the requesting origin
https://developer.mozilla.org/en-US/docs/Web/Security/Authentication/Passkeys
It useless to pretend to be the bank as you’ll get an assertion from the user you can’t replay and the user’s passkey implementation should spot the origin is wrong and refuse to sign it anyway (as I understand it).
 4·15 days ago
I think small open source commercial businesses would want this. Even if there’s overlap with Codeberg we need options for a healthy market. I hope you suceed and bookmarked for my own future hosting needs.
If by ISP NAT you mean you never have a unique external IP for your ISPs router then no, wireguard does nothing for you there.
 12·17 days ago
The author argues that passkey attestation would allow (eventually, via silent ratchet) any website to make demands about the software you run on your hardware. That would be a new thing and a reduction in freedom and privacy.
 1·20 days ago
Hamilton’s most famous contribution to the Apollo program came during the pivotal Apollo 11 mission to land on the moon in July of 1969. Moments before the Eagle module was set to land on the lunar surface, the onboard computer raised the alarm. It had detected a 1202 error: The computer was overloaded due to a fault in a hardware switch, and it was possible the system would not be able to handle the complex landing procedure.
But Hamilton and her team had engineered priority-driven software, able to shut down unnecessary background tasks in order to prioritize mission-critical tasks. Houston trusted Hamilton’s software and allowed the mission to proceed, and two men walked on the moon for the first time.
This is clearly depicted in the excellent film ‘First Man’ (2018) during the tense final landing when Neil Armstrong is visibly annoyed at the alarm but Houston, after a short delay, allow it to be switched off.

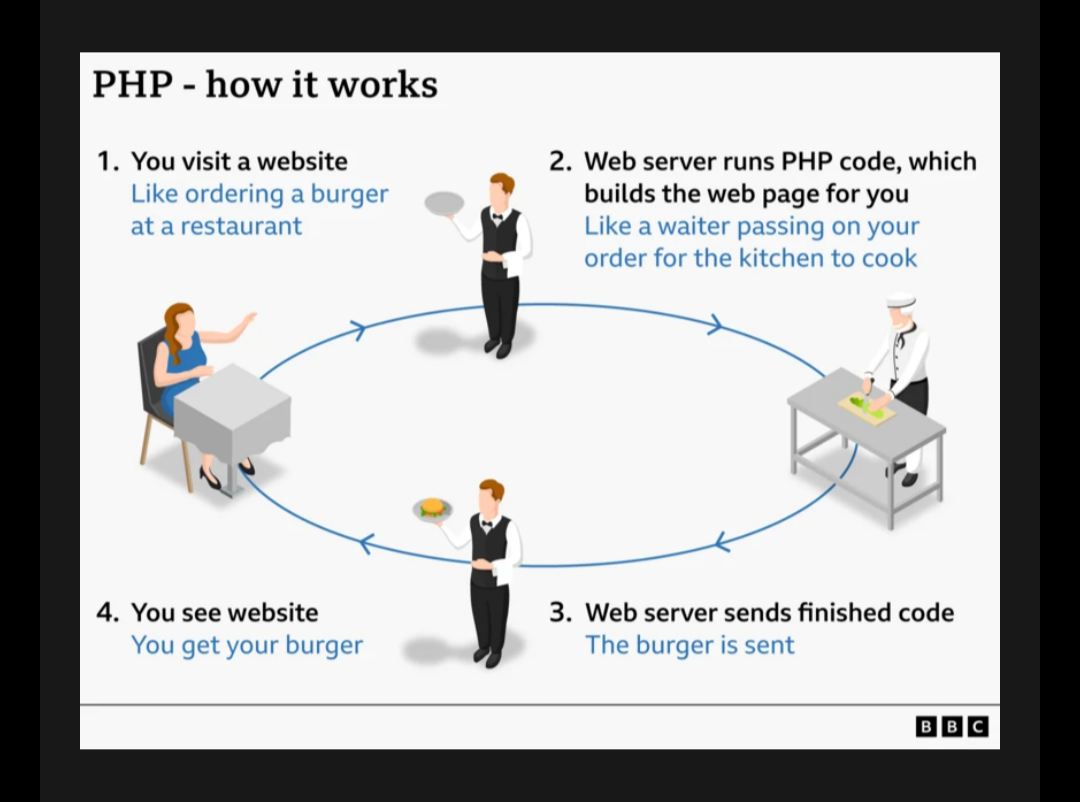

They didn’t move fast enough on it and others began circulating it. So they had to play catch up, hence the need to react before they had a patch.
https://thephp.foundation/blog/2026/10/21/todays-php-security-release-and-how-were-strengthening-php-security/